CrowdStrike's counter adversary operations chief Adam Meyers urges Korean banks to fix basic security gaps alongside AI defenses
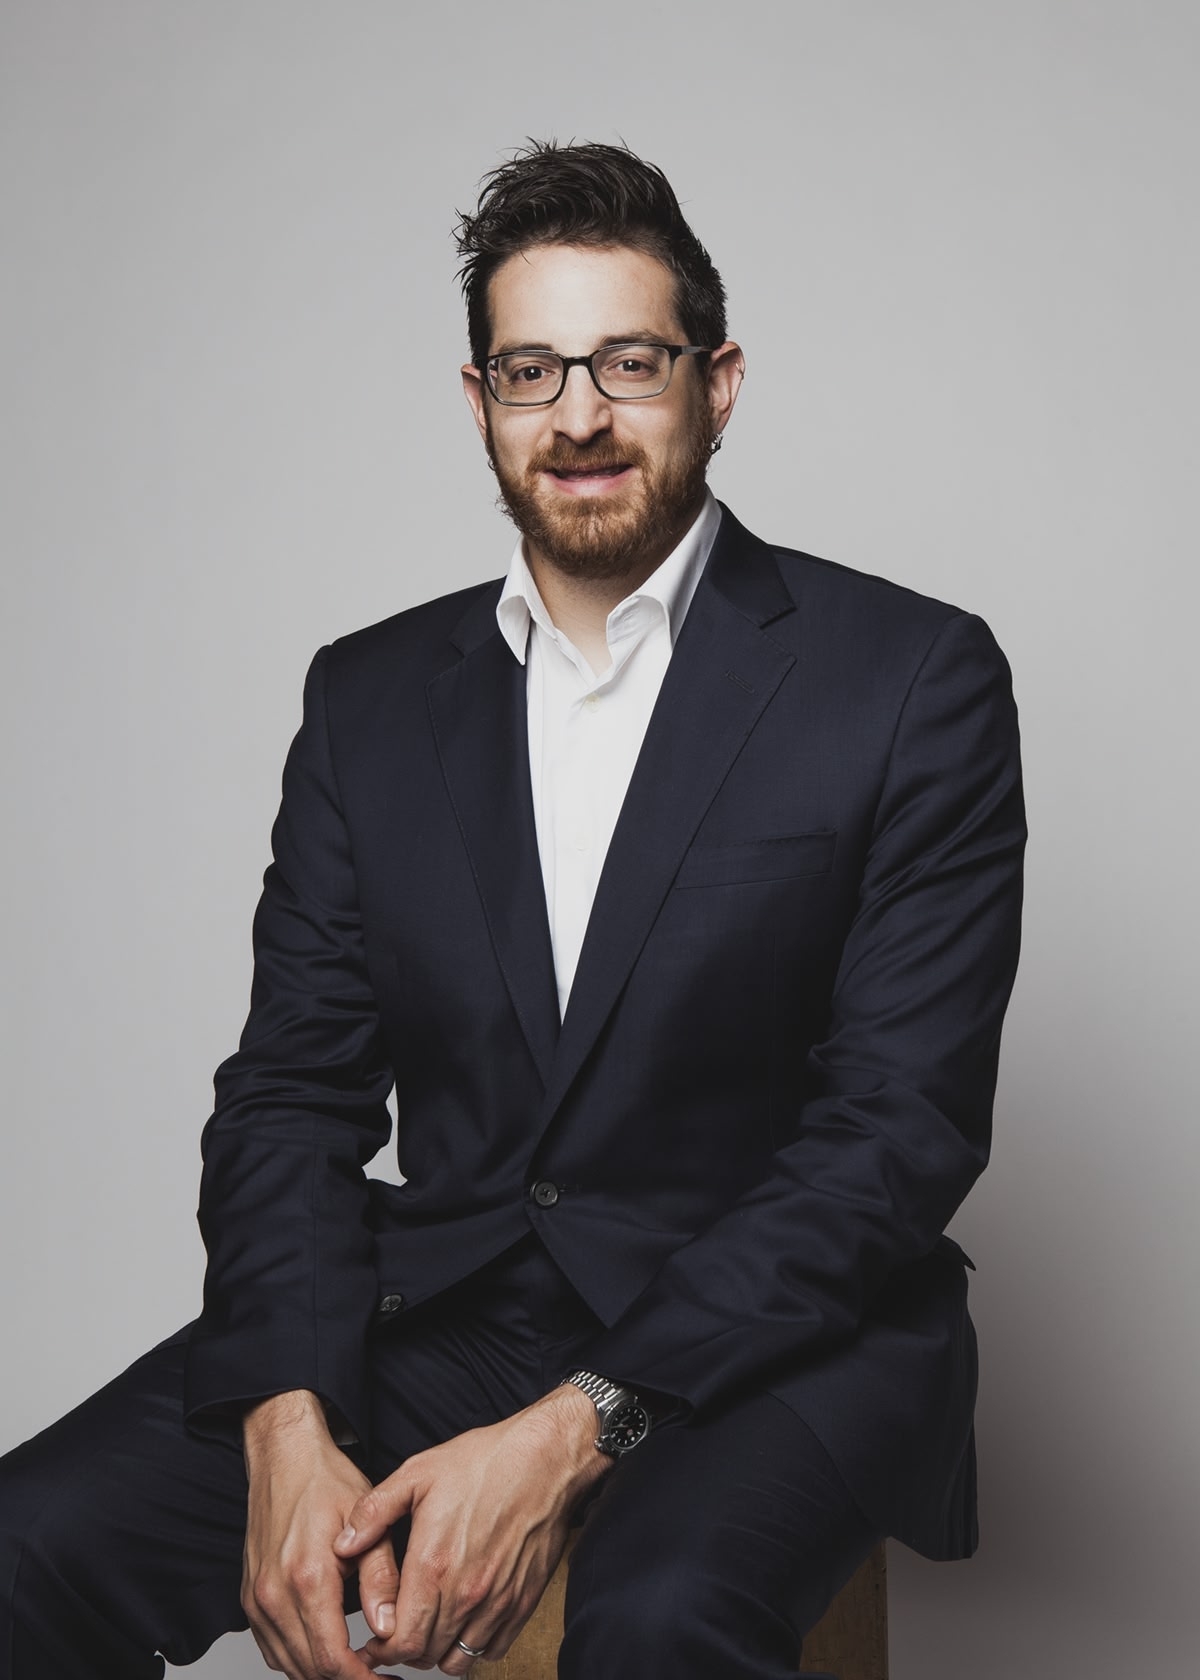
As South Korean banks pledge greater investment in artificial intelligence-powered cybersecurity following a series of breaches, the head of CrowdStrike's counter adversary operations says they must also address basic security weaknesses that allowed an inexperienced hacker to compromise financial institutions in the first place.
Adam Meyers, senior vice president of counter adversary operations at the US cybersecurity firm, oversees the team that helped uncover how AI was used in the attacks. Its Oct. 7 investigation report traced the attacker's servers and recovered AI session records that revealed how the intrusions were carried out. Meyers presented the findings to Korean reporters the following day.
Speaking in a follow-up video interview Tuesday, Meyers said, "AI gave the attacker the ability to pull off these attacks, but the fact that there was no security and poor hygiene on those systems enabled the attack to be successful."
AI supplied the skills, security gaps provided the opening
CrowdStrike had found that the attacker used ARTEX, a Chinese-developed AI penetration-testing tool, alongside large language models to target Korean financial institutions.
Asked what exactly the AI had enabled the relatively unskilled attacker to accomplish, Meyers replied, "All of it."
The tools handled tasks that previously demanded specialist knowledge, including finding website vulnerabilities and carrying out SQL injection attacks, which exploit weaknesses in how websites interact with databases.
"A lot of skills that a human previously needed to do that manually, the AI did for them," he said.
Several Korean financial institutions were breached through supporting systems used by employees or loan brokers rather than their core banking platforms.
"If they were not doing those things across every asset in their real estate, meaning they only tested the central banking system but did not test the employee systems or the API systems, then they left those systems exposed," Meyers said, referring to security testing and vulnerability assessments.
The country's financial regulators have confirmed hacking incidents at 16 financial companies, with personal information belonging to roughly 100,000 people exposed. Not all incidents have been linked to the same AI-assisted campaign.
AI defenses must go hand in hand with basic security
At Monday's parliamentary hearing, executives from major Korean banks pledged stronger cybersecurity measures, including expanded use of AI.
Asked whether banks should prioritize AI-powered defenses or improvements to existing security controls, Meyers replied, "They need to do both."
"The primary requirement is identifying vulnerabilities rapidly," he said. "Whether an organization accomplishes that through human teams or through AI matters less than maturing their processes, leveraging technology to locate and patch weaknesses, and training their personnel properly."
Recent parliamentary findings have drawn attention to those fundamentals.
Yegaram Savings Bank, which suffered a breach affecting more than 42,000 customers, was found to be running a decade-old version of database software with an unresolved vulnerability. It remains unclear whether that weakness was exploited in the attack.
In contrast, Woori Bank, which reported no data leak despite being targeted, cited additional employee authentication measures as a possible reason it avoided damage.
Meyers said banks should use AI-powered security testing tools to identify weaknesses before attackers exploit them, while maintaining monitoring systems capable of detecting suspicious activity across their networks.
He said the growing availability of such tools means companies can no longer rely solely on periodic security checks.
"Really, it becomes a matter of you needing to test before the bad guys test."
mjh@heraldcorp.com