Even diversionary cyberattacks now pose serious threats, overwhelming security teams
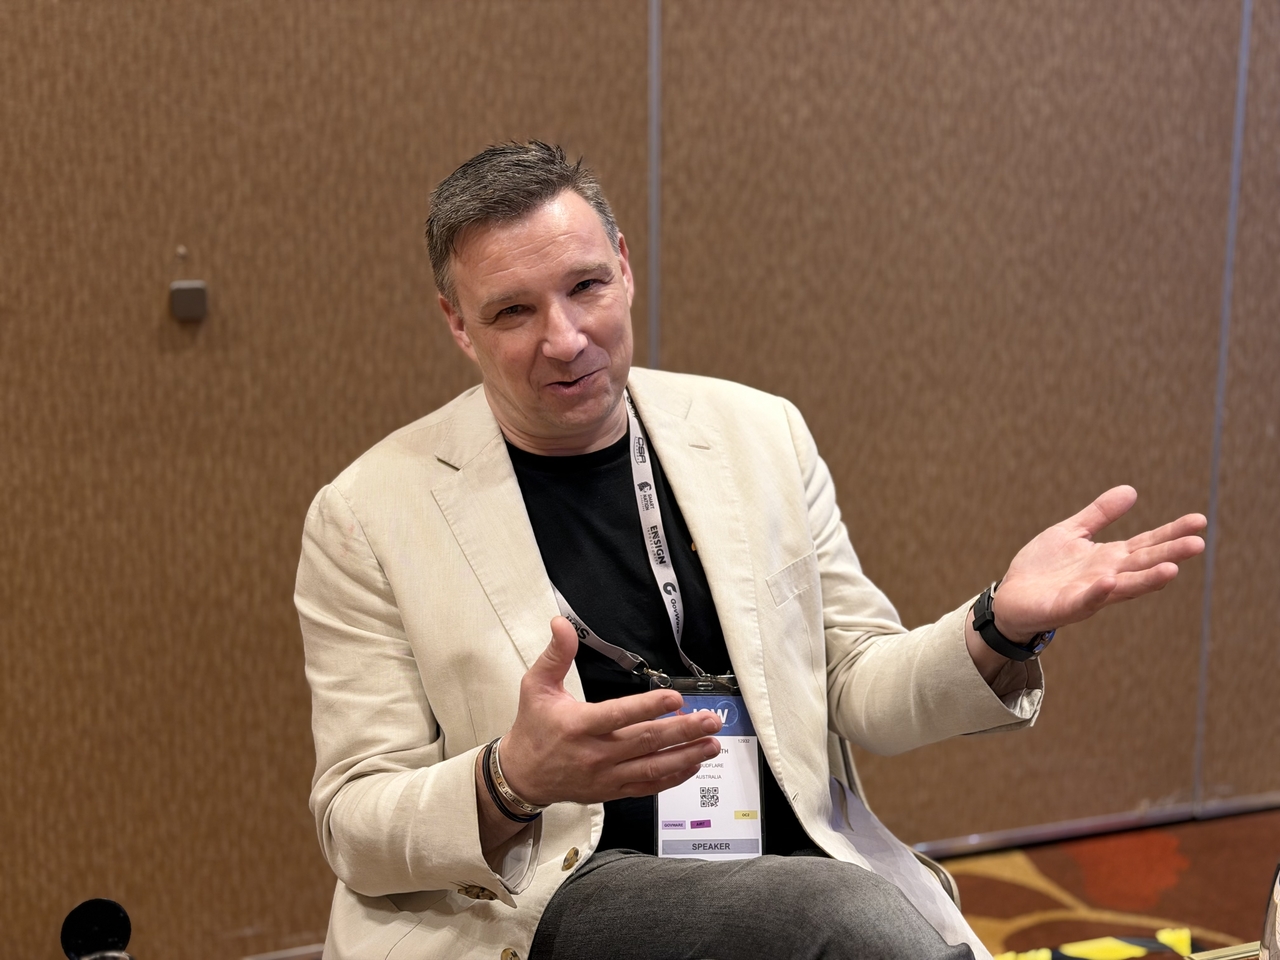
SINGAPORE — Cybercriminals once used relatively small attacks to distract security teams while pursuing more valuable targets. Artificial intelligence is changing that calculation, allowing hackers to launch sophisticated cyberattacks even when their main purpose is simply to keep defenders busy, according to a senior Cloudflare executive.
"These smoke bombs are now full-on cyberattacks because they can afford that. Because AI is doing all of that," said Volker Rath, field chief technology officer for the Asia-Pacific region at US cloud and cybersecurity company Cloudflare, in an interview with The Korea Herald during Singapore International Cyber Week on Thursday.
Rath said such diversions previously required considerable human effort. Now, AI allows attackers to repeat sophisticated operations on a scale that was difficult to sustain manually.
"If every smoke bomb is a full-on cyberattack, I cannot ignore them," he said.
An apparent distraction could itself cause serious damage, while investigating every incident risks overwhelming security analysts.
"The problem we see here is that cyber teams are getting burned out," Rath said.
He assessed that companies need to automate more of their threat detection and response, allowing analysts to concentrate on incidents requiring human judgment.
AI's speed can also give attackers away
Yet Rath said automated attacks can sometimes reveal themselves through unusually rapid activity.
"The weakness of AI is quite often it's too good," he said.
He described a program checking 20 potential security weaknesses in just two seconds, a pattern that could alert defenders to someone searching for a way into their systems.
"If one process does 20 checks in two seconds, first of all, who checks all of these things?" he said.
Rath pointed to honeypots — decoy systems that alert security teams when intruders interact with them — as one way to detect suspicious activity early.
Rapid scanning is not unique to AI, and attackers can adjust their behavior to avoid detection. But spotting unusual activity also depends on whether companies are properly monitoring their systems.
Rath recalled speaking with a bank that had invested in security monitoring technology but was not sending important system logs of network activity to its central monitoring platform. Without those records, analysts had less information to identify suspicious behavior or investigate potential intrusions.
Banks struggle to keep pace
Rath said banks also struggle with lengthy purchasing and implementation processes that can leave defenses struggling to keep pace with changing threats.
He described how banks can spend months selecting security products, configuring them and securing approval for changes. Even when the technology is capable of stopping an attack, the threat may have evolved before the system is fully deployed.
"So even if the best tool in the world is too slow," he said, it cannot provide the protection organizations need.
Rath also questioned banks' emphasis on regulatory compliance, arguing that passing an audit does not necessarily mean an institution can withstand an actual cyberattack.
A bank might satisfy an audit by regularly backing up its data, for example, yet be unable to recover from ransomware if attackers compromise those backups.
"You are compliant, but you're still not resilient," he said.
The concern has particular relevance in South Korea, where the Financial Services Commission said last week that a review of 555 financial companies identified security shortcomings at 130, including gaps in monitoring and access controls.
Rath argued that companies should make better use of safeguards they already possess, including threat modeling to identify potential weaknesses and Zero Trust controls that restrict access until users are verified.
But he acknowledged that encouraging customers to maximize existing investments does not always align with cybersecurity vendors' commercial interests. "It's not great for security vendors," he said. "Picking a low-hanging fruit is typically utilising what you already have and get more value out of your existing investment."
mjh@heraldcorp.com